
Uganda must strengthen its cyber resilience as the country’s economy and public services become increasingly dependent on digital technologies, the Uganda Communications Commission (UCC) has warned.
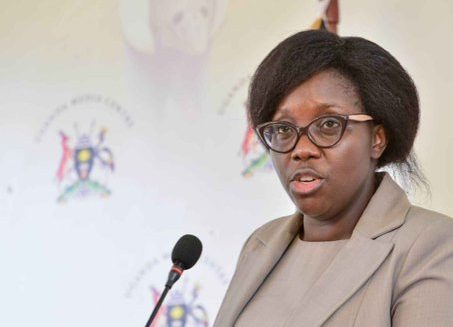
Dr Christine Mugimba, the UCC Director of ICT and Research, said the growing reliance on digital infrastructure means cybersecurity can no longer be treated merely as a technical issue, but as an important part of protecting the economy and public confidence.
“Cyber resilience must increasingly be viewed as economic resilience,” Mugimba said.
She was speaking at the Information Security Conference (IFOSEC) 2026 organised by the ISACA Kampala Chapter under the theme “Securing the Future Through Digital Trust.”
Her remarks come at a time when Ugandans are increasingly relying on digital platforms for mobile money payments, banking, e-commerce and other services, increasing the consequences of disruptions, fraud, data breaches and other cyber threats.
According to the National Information Technology Authority-Uganda (NITA-U), the officially measured ICT sector contributed about 2.54 per cent of Uganda’s gross domestic product at constant prices in the financial year 2024/25.
The sector’s real value added was estimated at about Shs4.13 trillion, while its value at current prices reached approximately Shs4.78 trillion, highlighting the growing contribution of ICT to economic activity.
Mugimba said Uganda had already established important foundations for cybersecurity, including enabling legislation, regulatory institutions, Computer Emergency Response Team capabilities, standards, cybersecurity laboratories and exercises, as well as mechanisms for threat monitoring and incident coordination.
Through the Uganda Communications Commission and the Uganda Computer Emergency Response Teams, she said, the country was detecting threats, coordinating incident responses, assuring compliance and preparing institutions through technical training, cyber drills, public awareness and child online protection programmes.
However, she said these capabilities should be regarded as a foundation rather than the destination.
“The real measure of success is not how many tools we own, but whether threats are detected early, vulnerabilities remediated faster, incidents contained more effectively, services restored more quickly, and whether the majority of the people who are not in this room, citizens, have greater confidence in the digital services they use,” Mugimba said.
She said digital trust was particularly important because communications infrastructure now underpins several critical sectors of the economy.
A citizen, she said, must be confident that money sent electronically reaches the intended recipient, while businesses need assurance that their digital platforms will remain available and secure.
Government systems, she added, must also be protected from compromise, while the increasing use of artificial intelligence is raising questions about whether voices, images and videos circulating online are genuine.
“Cybersecurity, therefore, is not only about protecting computers and networks. It’s about protecting and building confidence in the digital economy,” Mugimba said.
She called for stronger protection of critical communications infrastructure, taking into account the growing interdependence between telecommunications, financial services, cloud environments, government platforms and other critical sectors.
Mugimba also urged institutions to improve the speed and quality of threat-information sharing so that malicious infrastructure, vulnerabilities, compromised credentials and active cyber campaigns can be addressed quickly.
She said security should be incorporated into technology from the beginning rather than introduced after systems have already been developed.
“During design, procurement, development, integration and deployment, it should not be an afterthought,” she said.
She further called for responsible governance of emerging technologies, including artificial intelligence, 5G and beyond, cloud computing, the Internet of Things and software-defined infrastructure.
But Mugimba said technology and regulation alone would not be sufficient without investment in people capable of operating and securing digital systems.
“Technology without the skills to operate, secure and sustain it cannot deliver its full value,” she said.
As the ICT sector regulator, Mugimba said UCC expects organisations within the communications ecosystem to understand their risks, protect critical infrastructure, identify and promptly address vulnerabilities, report significant incidents and safeguard consumers and their information.
She also called for institutions to manage third-party and supply-chain risks, test their response and recovery capabilities and invest in competent cybersecurity personnel.
“Cybersecurity must be treated as a continuous governance responsibility, not an annual compliance exercise,” Mugimba said.
She said Uganda had established important cybersecurity foundations, but the next test was building resilience at scale as the country became more connected, data-driven and technology-enabled.
Mugimba cited the International Telecommunication Union’s Global Cybersecurity Index, which she said points to capacity development as an area where Uganda has an opportunity to improve.
She called for simultaneous investment in people, institutions, technology, regulation, cooperation and accountability.
The UCC director also urged the sector to expand mentorship, apprenticeship and partnership opportunities and develop practical skills in cloud telecommunications and artificial intelligence, including the ability to govern the cyber risks associated with the technologies.
The emphasis on digital trust was echoed by Maurice Taremwa, president of ISACA Kampala, who said the growth of digital systems had fundamentally changed the responsibility of information-security professionals.
Taremwa said that when the conference started 15 years ago, mobile money was still emerging, cloud computing was largely a debate about whether organisations could trust servers they could not physically see, and data-protection laws were not yet established.
Today, he said, digital systems hold the savings of millions of households, the tax base of economies, citizen identities and health records.
“The responsibility has grown,” Taremwa said, challenging information-security professionals to consider whether their capacity and approach had grown with it.
He said digital trust was not evenly distributed because ordinary users often have limited ability to verify the systems they depend on.
A market vendor receiving a mobile-money payment cannot audit the infrastructure through which the transaction passes, while a small business using cloud accounting software may not be able to examine the security controls of its provider.
“They trust because they have no alternative,” Taremwa said.
He described information-security professionals as guardians of public confidence in systems that ordinary users may never see.
“We are not the guardians of systems. We are the guardians of the people’s confidence in systems they will never see,” he said.
Taremwa urged participants to ensure that cybersecurity decisions consider people outside the conference room, particularly users who may never read a security policy or understand the technical controls behind the services they use.
He said the value of the annual conference should ultimately be measured by what changes after participants return to their workplaces.
“The conference is not measured by the quality of the speakers or the comfort of this venue. It is measured by what changes afterwards,” Taremwa said.